Meta's Live Hacking Event at ekoparty 2026
The other Live Hacking Event that week was Meta's. 46 reports, the toughest program out there, and one uncomfortable truth: here, privacy is what pays.
In October I was at ekoparty, in Buenos Aires, and took part in Meta's Live Hacking Event. It was by far the hardest one I've done.
Meta's program (bugbounty.meta.com) is one of the most demanding out there: some of the best hunters in the world take part in it, and the bar for something to count as a finding is very high. It's not a place to show off, it's a place to measure yourself. That's exactly why I wanted to run my system, DS-AI, there: if it worked against Meta, it worked against anyone.
For authenticated testing they gave us access to internal tooling, Muse and FBDL among them. I leaned on FBDL a lot. That level of access is a different thing: you see the real surface, not the one exposed from outside.
It was my first time in Meta's program, so I started from zero, no reputation, no history, which counts for a lot in a place like this. I ended up sending 46 reports. Many were valid but not paid, and that's the part worth understanding. Meta's focus is privacy. A finding can be a real, well-hunted bug, and if it doesn't touch user data it falls outside the bounty anyway. It's a hard rule, but an honest one, and it forces you to think differently about what impact means.
It's all still under review. One has already been paid, and the six that are triaged will likely add points and rewards once they close. That's the picture today: six triaged, four in the queue, and one on hold because Meta asked me for more information. Since I came in with no history, every report that lands moves the table.
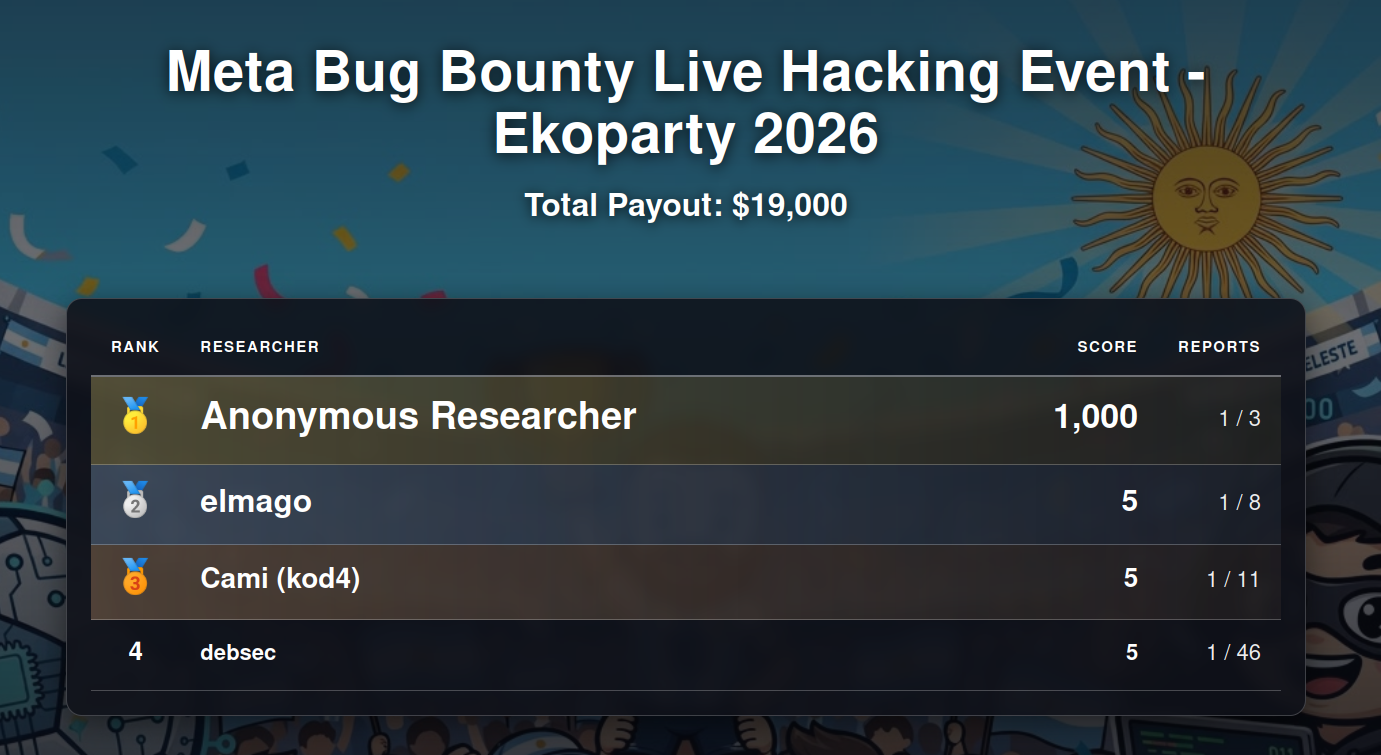
How the table stands today, still under review.
What I found, I won't tell: it's still in process and under coordinated disclosure, as always.
Two things stay with me. That the system held up in the hardest place there is. And that every program has its own rules: reading them well, and accepting when a bug doesn't count, is part of the craft too.
This isn't over: as Meta closes out the reports, I'll update the numbers here.